Why Traditional Perimeter Security No Longer Works
For decades, enterprise security was based on a simple notion: build a strong perimeter around your network, and everything inside is trusted, everything outside is not. Firewalls, VPNs, and intrusion detection systems were deployed at the edges of corporate networks, creating “walls” to keep threats out. This castle-and-moat model worked well when employees, applications, and data resided primarily within local, easily defined networks—or behind corporate firewalls.
However, the nature of work and IT infrastructure has radically shifted. According to Gartner, 70% of enterprise workloads are now running in public cloud environments (2023), and over 85% of organizations support hybrid or fully remote workforces (FlexJobs Remote Work Statistics, 2024). Users and devices access resources from a multitude of locations, across home broadband, mobile networks, and public Wi-Fi. Corporate applications have moved to SaaS, and data is spread across cloud, edge, and on-premises systems. The traditional network perimeter has effectively dissolved—rendering the old approach not just obsolete, but risky.
Attackers have noticed. Verizon’s 2023 Data Breach Investigations Report found that 74% of all breaches involve the human element—phishing, credential theft, or exploited remote access. Once inside a weakly segmented network, attackers can move laterally, often undetected, to steal sensitive data or deploy ransomware. The recent surge in supply chain and SaaS-based attacks highlights how traditional perimeter security fails to protect modern, distributed assets.
Enter Zero Trust: A Paradigm Shift
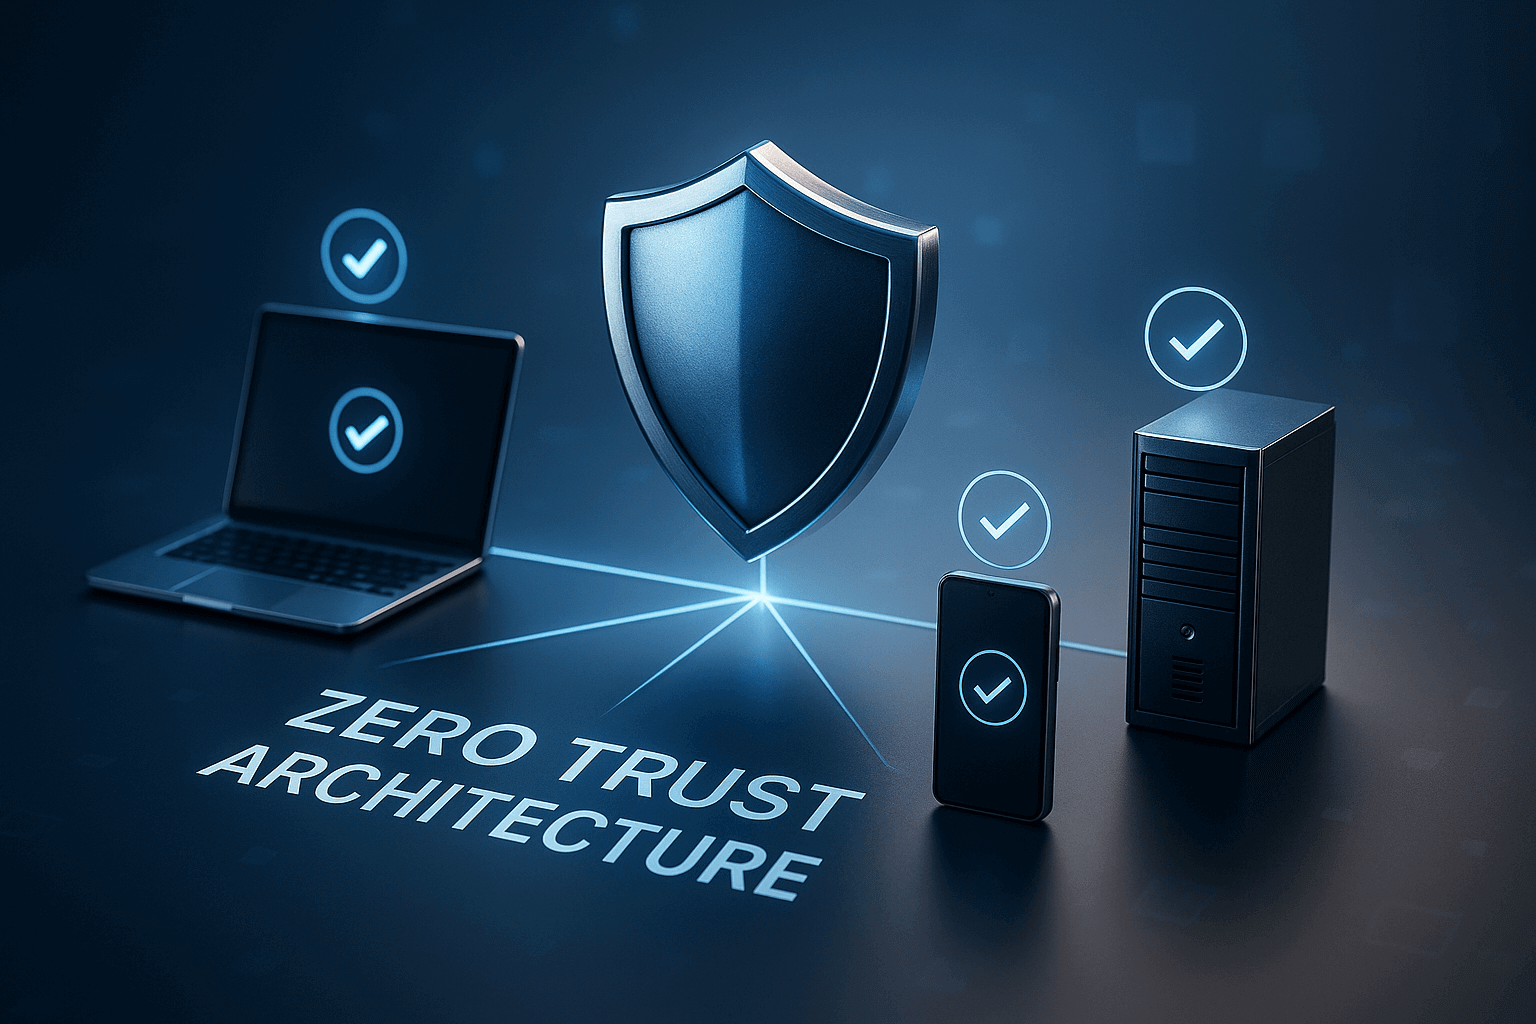
Zero Trust Architecture (ZTA) fundamentally rethinks the way enterprises approach security. Instead of assuming that anything inside the network should be trusted, Zero Trust takes the opposite stance: Never trust, always verify.
All users, devices, applications, and network flows are treated as potentially hostile. Every request for access—no matter the origin or destination—is inspected, authenticated, and authorized based on granular policy. This approach dramatically reduces the risk posed by compromised accounts, rogue insiders, and lateral movement by adversaries.
Gartner predicts that by 2025, 60% of organizations will phase out their VPNs in favor of Zero Trust Network Access (ZTNA) models—up from just 10% in 2021. ZTA is no longer cutting-edge; it’s swiftly becoming table stakes for enterprises seeking to secure digital transformation, remote work, and compliance goals.
Key Pillars of Zero Trust Architecture
- Continuous Verification: Every access request is authenticated and authorized in real time using multifactor authentication (MFA), device compliance checks, behavioral analysis, and risk scoring.
- Least-Privilege Access: Users and applications are granted only the minimum level of access necessary—nothing more.
- Micro-Segmentation: Resources are broken into isolated segments. Traffic between segments is tightly controlled and monitored, minimizing the blast radius of any breach.
- Policy-Based Access Control: Access is granted not on network location, but on dynamic factors such as user identity, device posture, role, and context.
- Visibility and Analytics: Every interaction is logged and analyzed for abnormal activity that could signal a compromise or policy violation.
Implementing Zero Trust—A Practical Roadmap
Adopting Zero Trust is not a one-off “big bang” project, but a strategic, phased journey. Here are the essential steps—and best practices—to build a robust Zero Trust foundation without sacrificing productivity or user experience:
1. Map Your Critical Assets and Flows
Begin by identifying your organization’s sensitive data, applications, and workflows. Catalog which users and devices require which access, and trace the data flows between them (north–south and east–west). Solutions like Cloud Security Posture Management (CSPM) and Asset Inventory systems can automate much of this discovery, reducing manual overhead and blind spots.
2. Deploy Strong Identity and Access Management (IAM)
Robust, federated identity is foundational. Implement Single Sign-On (SSO) and Multi-Factor Authentication (MFA) for all internal and external users. According to Microsoft, enabling MFA alone can prevent 99.9% of account compromise attacks. Use context-aware policies—evaluating device health, location, and risk factors—before issuing authorization tokens.
3. Enforce Device Compliance and Security Posture
Every device—corporate or BYOD—should be evaluated for compliance before granting access. Endpoint detection and response (EDR) platforms, unified endpoint management (UEM), and mobile device management (MDM) are critical for real-time compliance checks (patch level, malware status, encryption, etc.). Devices that deviate from policy can be quarantined or blocked until remedied.
4. Implement Micro-Segmentation and Network Controls
Rather than wide-open, flat internal networks, apply micro-segmentation (using next-gen firewalls, software-defined perimeters, or SDN). This approach creates fine-grained “zones of trust” with policies enforced at the application layer. For example, finance users can only access financial systems, HR staff only HR applications. East-west traffic between segments is scrutinized continuously.
5. Adopt Zero Trust Network Access (ZTNA)
ZTNA replaces legacy VPNs—which often grant overly broad network access—with software-defined, context-driven access to applications. Users are authenticated continuously; their activity is monitored, and access can be revoked instantly based on changes in risk score. Major vendors (like Okta, Microsoft, Zscaler, or Palo Alto) offer scalable ZTNA solutions with seamless user experience.
6. Leverage Continuous Monitoring and Analytics
With Zero Trust, every transaction generates telemetry. Centralize logs (using SIEM or XDR tools) for correlation and real-time anomaly detection. Modern machine learning models can flag suspicious behavioral patterns—such as impossible travel, unusual file exfiltration, or privilege escalation—before damage occurs. In 2023, organizations deploying security analytics reported a 45% reduction in dwell time for attackers, minimizing breach impact (IBM Cost of a Data Breach Report).
Balancing Security With Productivity and User Experience
One common concern about Zero Trust is perceived friction—will employees face endless authentication prompts or application slowdowns?
Here’s how to maintain great user experience while securing your enterprise:
- Use Adaptive Authentication: Risk-based conditional access means that low-risk actions from compliant devices can be “low friction,” while risky scenarios (new device, high-value transaction, anomalous location) trigger additional verification.
- Seamless SSO & MFA: Choose modern identity platforms offering passwordless authentication (such as FIDO2, biometrics, or push notifications). Reduces password fatigue and increases both usability and security.
- Agentless Access Where Possible: Implement browser-based or cloud-native ZTNA solutions that don’t require end-user agents, speeding onboarding and compatibility across device types.
- User Education: Empirical studies show that users familiarized with Zero Trust workflows are 40% less likely to attempt risky workarounds, improving both security and satisfaction.
Metrics and Outcomes: Zero Trust in Action
- Data Breach Reduction: Forrester reports organizations with mature Zero Trust architectures see up to 50% fewer security incidents compared to peers with traditional models.
- Ransomware Resilience: Micro-segmentation and continuous authentication contain ransomware outbreaks to a single enclave, limiting operational impact (mean time to contain (MTTC) reduced by 33% – Ponemon Institute, 2023).
- Faster Remediation: Zero Trust organizations detect and remediate incidents twice as fast (IBM Security, 2023), thanks to enhanced visibility and automated controls.
- Regulatory Compliance: Zero Trust controls map directly to GDPR, HIPAA, and PCI-DSS requirements for least-privilege, access logging, and breach minimization.
Conclusion: Zero Trust is the New Productivity Enabler
In a world where users, devices, workloads, and threats are distributed everywhere, the consequences of relying on perimeter-based defenses are stark. Zero Trust isn’t just a security upgrade; it’s a business enabler. It reduces risk, simplifies compliance, and—when implemented thoughtfully—empowers employees to work flexibly, securely, and productively from anywhere on any device.
The journey to Zero Trust begins with identity, expands across networks and devices, and matures with continuous verification, analytics, and automation. Organizations investing in Zero Trust today report not just fewer breaches, but faster incident response, smoother access to cloud and remote apps, and greater organizational agility.
Ready to future-proof your security architecture? Adopt Zero Trust, verify everything, and unlock the benefits of secure productivity in the distributed enterprise era.